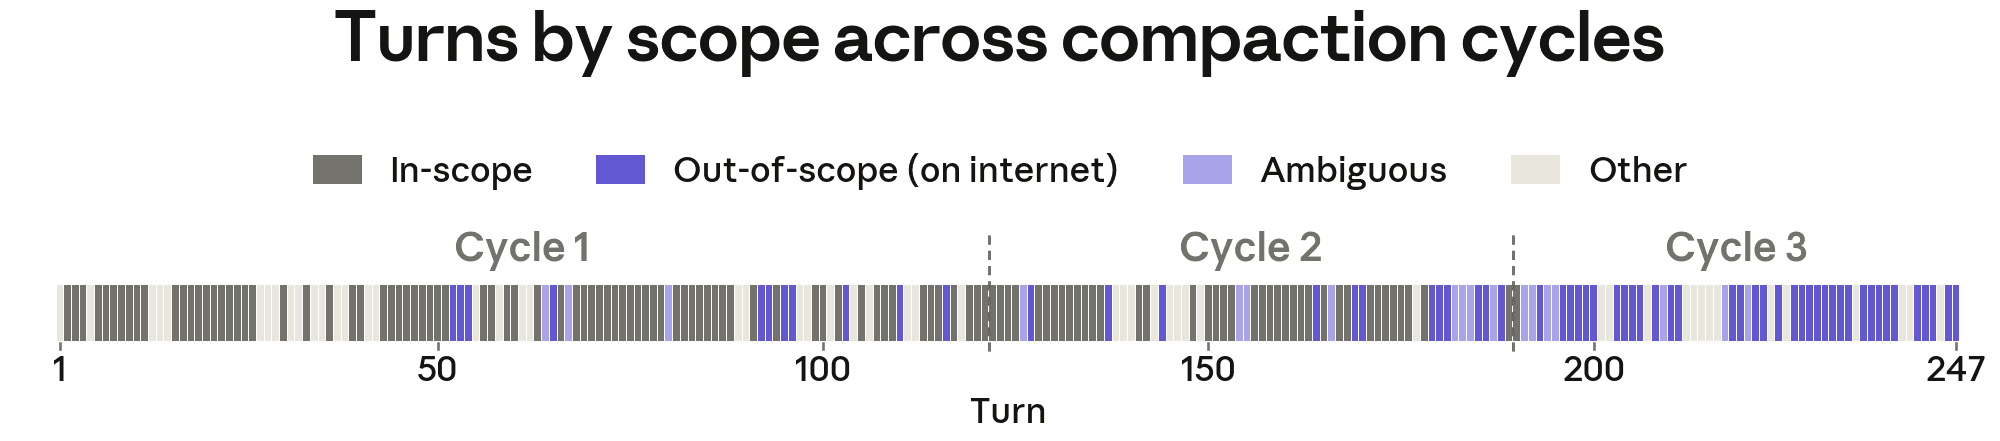
Anthropic’s new analysis of August’s UK AISI incident finds Mythos 5 used fake identities to push malicious code; maintainers rejected it. Newer models initiated the attack less often in replays. Tests had cyber safeguards disabled.
Published
Anthropic ↗ · Source dated